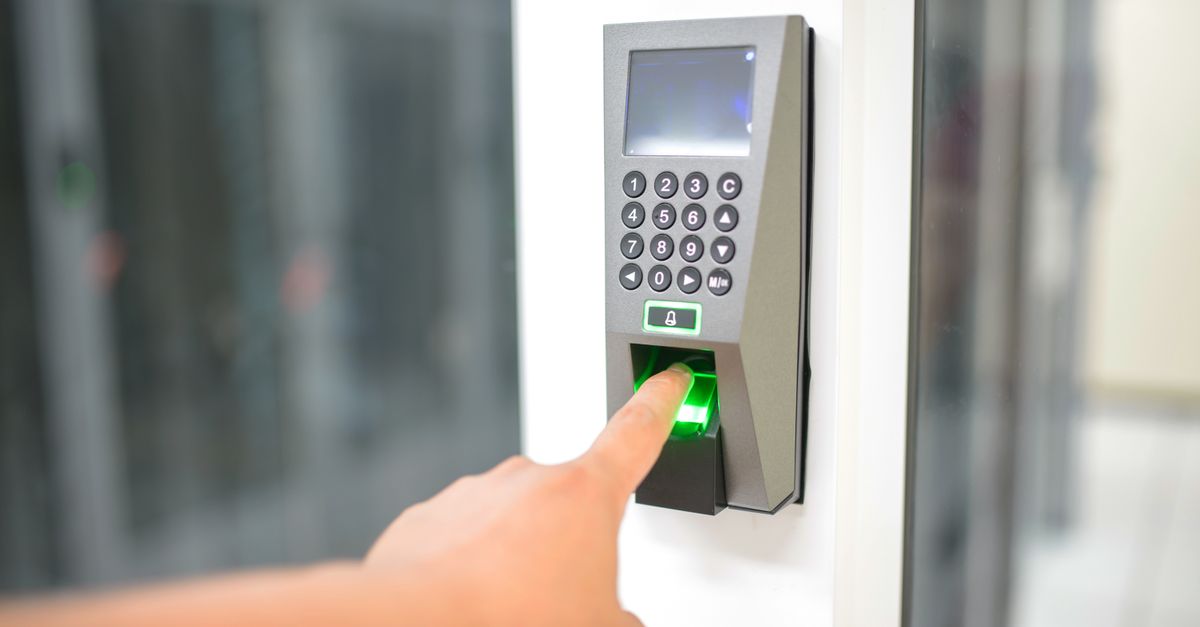
More than 23 million people who sign into UK government services can now do it with a fingerprint or a face scan instead of a password, after the Cabinet Office confirmed on September 14 that passkeys are rolling out widely across GOV.UK One Login following a 300,000-user trial. The announcement itself is small: an optional login upgrade, still sitting alongside the password it is meant to replace. The coverage around it is where the more interesting story sits, and it is not fully the story any single outlet told.
What GOV.UK Actually Announced
According to the government’s own release, nearly one in ten daily sign-ins to GOV.UK One Login, the single account UK residents use for services including State Pension checks, tax management, and childcare support, are already happening through a passkey rather than a username, password, and text-message code. The government says the switch is already saving taxpayers close to 600 pounds a day in SMS costs and that passkey logins complete roughly eight times faster than the password-plus-2FA flow it is nudging users away from. Stephanie Peacock, the Digital Government Minister, put the pitch in consumer terms: “Nobody enjoys hunting for a forgotten password or waiting for a text message code just to check their tax return or renew a document.” Jonathon Ellison, the National Cyber Security Centre’s director for national resilience, framed the security case the same way most vendors do when they pitch passkeys: “The introduction of passkeys for GOV.UK One Login will give users a faster, simpler and more secure way to sign in.”
How the Trade Press Read It
Three independent accounts of the same announcement chose three different emphases, and read together they say more than any one of them does alone. The Register’s coverage led with the headline framing that UK.gov is “killing off passwords for 23 million users,” treating the rollout as the leading edge of an elimination, not an addition. PublicTechnology, the UK public-sector trade title, covered it as an incremental feature update: biometric passkeys arriving inside an existing system, consistent with how GOV.UK One Login has rolled out other authentication options in the past. Mobile ID World took a third angle entirely, tying the passkey news to the government’s separate, previously announced 2027 deadline for GOV.UK One Login: the point at which the older Government Gateway sign-in system is retired and One Login becomes, per the government’s own stated plan, the only way to access central government digital services.
Media Partner
Worth noting what none of the three accounts did: challenge the government’s own numbers. The eight-times-faster claim, the roughly 600-pounds-a-day SMS savings figure, and the nearly-one-in-ten adoption rate all trace back to the same release, restated rather than independently verified by any of the outlets covering it. That is not unusual for a policy announcement covered on the day it lands, but it means the “success story” framing common to all three pieces, including The Register’s more skeptical headline, is still built entirely on the government’s own self-reported metrics rather than any external audit of GOV.UK One Login’s passkey implementation.
None of the three accounts is wrong. But only Mobile ID World’s framing puts today’s opt-in convenience feature inside the timeline that actually matters: passkeys are not a permanent alternative sitting next to passwords indefinitely. They are the front edge of a consolidation that, by the government’s own 2027 target, collapses the authentication paths into GOV.UK One Login and nothing else. The Register’s “killing off passwords” headline is more accurate about where this is heading than PublicTechnology’s incremental-feature framing suggests, even though nothing in this week’s announcement forces anyone off a password yet.
The Through-Line the Coverage Missed
Put the three accounts together and the actual story is not “passwords are being phased out.” It is that a government is about to make one authentication system, secured one way, the sole gateway to pensions, tax records, benefits, and identity verification for over 23 million people, and the security discussion happening this week is entirely about the convenience and phishing-resistance of the login method, not about what it means to concentrate that much access behind a single identity provider. A phishing-resistant passkey is a real improvement over a password that can be typed into a fake site. It does nothing to reduce the blast radius if GOV.UK One Login itself, or the device-bound key material behind it, is ever compromised, misconfigured, or subject to an outage. Centralizing authentication is a tradeoff, not a pure security win, and none of this week’s coverage, including the government’s own release, frames it as one.
That gap matters more given what CyberTech has already reported this week. Microsoft disclosed, and CyberTech covered in a brief on September 13, a live campaign in which attackers use fake passkey enrollment prompts to hijack Microsoft cloud accounts, not by breaking the cryptography behind passkeys but by social-engineering victims into registering an attacker-controlled authenticator during account recovery. The lesson from that campaign is that passkeys remove one attack path, credential phishing at the login page, while leaving the account-recovery and enrollment flow around them exactly as exploitable as before. GOV.UK’s own release says nothing about how One Login handles device loss, recovery, or re-enrollment at the scale of 23 million users, and none of this week’s press coverage asked.
There is a mechanical reason passkeys close the phishing gap that passwords never could: a passkey is bound to the specific website domain it was created for, using public-key cryptography where the private key never leaves the user’s device. A fake login page can display a password field and simply record whatever a victim types into it. It cannot make a browser hand over a passkey’s private key, because the browser checks the domain before it will even offer the credential. That is a genuine, structural improvement, not a marketing claim, and it is the reason the National Cyber Security Centre has pushed passkeys as its preferred authentication method. But cryptographic domain-binding only protects the moment of login. It says nothing about how a user proves who they are when they lose a device and need a new passkey issued, which is precisely the seam the Microsoft campaign targeted, and precisely the seam a government service used by 23 million people, many of them not security-sophisticated, will need answered at scale.
What This Means for the Security Leader
For CISOs watching the public sector as a bellwether, not just a UK story: GOV.UK One Login is functioning as one of the largest live tests of population-scale passkey adoption anywhere, and it is happening under a hard 2027 mandate, not a voluntary migration. Enterprise security leaders evaluating their own FIDO2 or passkey rollouts should treat the account-recovery and re-enrollment path, not the login prompt itself, as the control that actually needs hardening before scaling to this size. A passwordless system is only as phishing-resistant as its weakest fallback path, and the fallback path is where the September 13 Microsoft campaign, and most passkey-related social engineering CyberTech has tracked this year, has already moved. The same logic applies to organizations consolidating single sign-on around one identity provider for compliance or cost reasons, a pattern CyberTech has argued elsewhere concentrates risk in the identity-verification process itself rather than removing it.
What To Do Now
Security teams evaluating a passkey or FIDO2 rollout should audit the account-recovery flow with the same rigor applied to the primary login path, since that is the fallback attackers are already targeting in the wild. Anyone consolidating authentication behind a single identity provider, public or private sector, should document what happens if that provider is unavailable or compromised, not just what happens when it works. And any organization treating “passwordless” as a finished security upgrade should confirm that claim only covers the login prompt, not the enrollment, recovery, or help-desk processes that sit around it, since those remain the paths phishing campaigns are adapting to exploit.
Source: GOV.UK